AI agent governance is the set of access controls, audit logs and approval rules that determine what AI agents can see and do inside a company, and who is accountable when they act. It is how enterprises let agents read data and change real systems like Salesforce, Jira or Slack without creating security, compliance or operational risk.
AI governance has become a buzzword, and the term is used loosely. This guide explains what governance means specifically for AI agents, why it is harder than governing traditional software, the three controls every program needs, how to decide which actions need human approval, and how to put it into practice.
AI governance in general is the set of policies, processes and controls that keep AI systems, including models, applications and agents, safe and compliant. Organization-level frameworks such as the NIST AI Risk Management Framework, ISO/IEC 42001 and the EU AI Act set expectations for how a company manages AI risk as a whole.
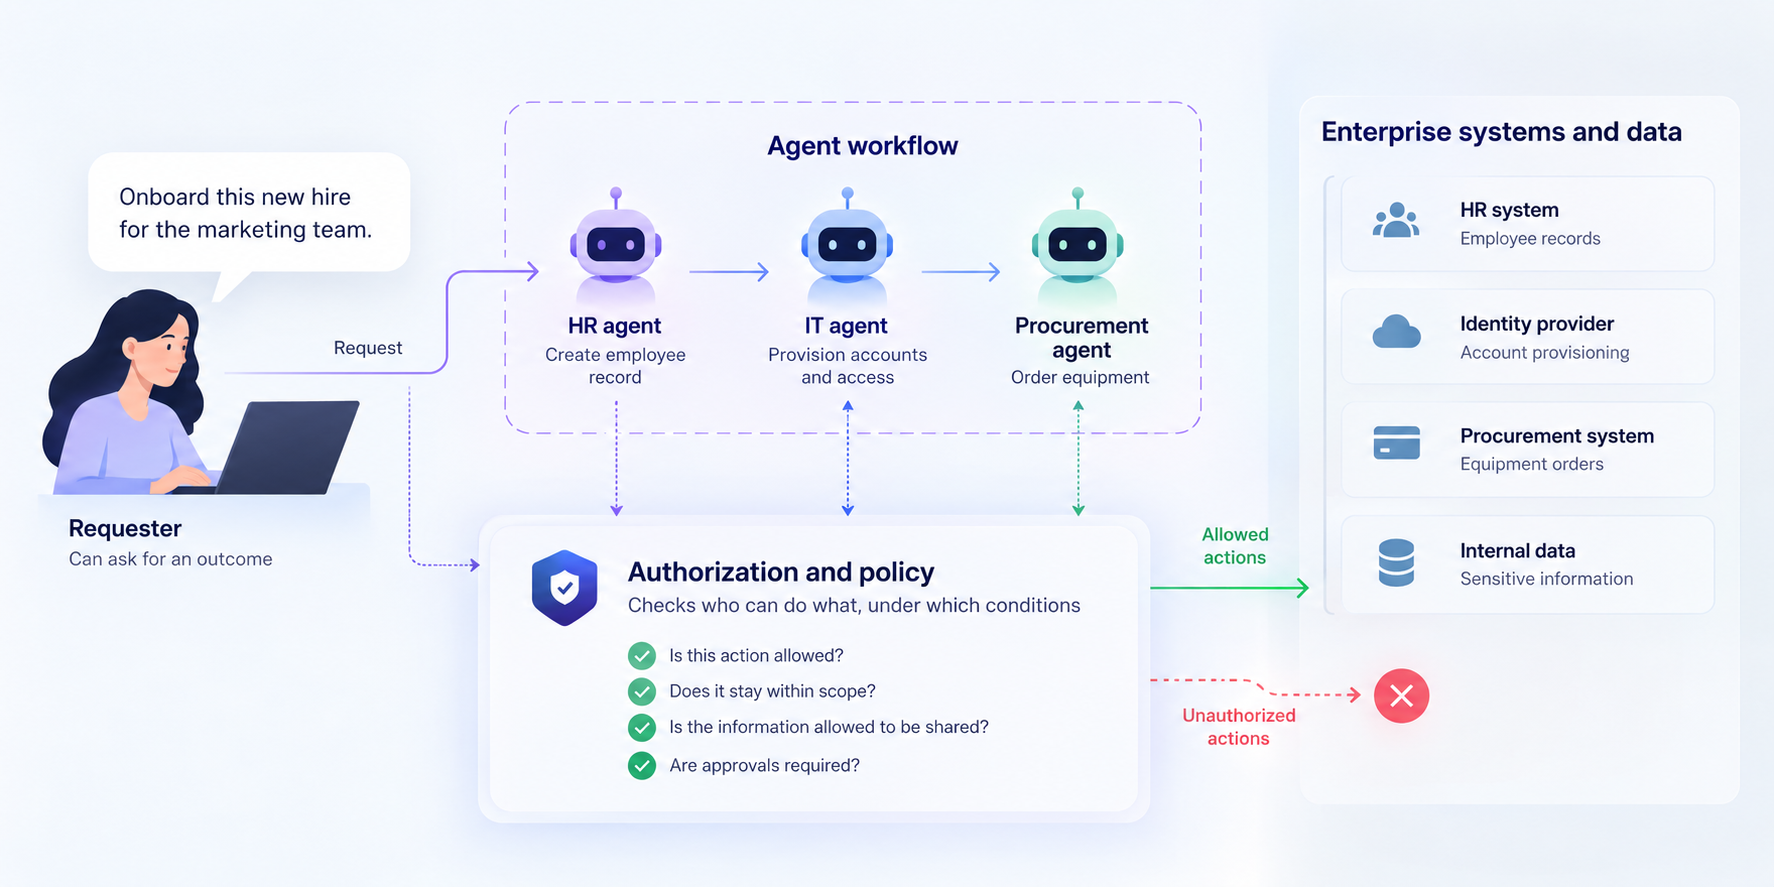
AI agent governance is the operational layer underneath. It answers concrete questions: Which agents exist? Who owns each one? What data can it read? What can it change? Which actions need a person to approve them? Where is the record of what it did? Existing compliance frameworks like SOC 2 touch on this only indirectly, through how systems handle data. Agents are new enough that most companies have to build the answers themselves.
Traditional bots and scripts do the same thing every time, so you can review the code once and trust the behavior. Agents are non-deterministic: the same agent can act differently depending on the prompt, the documents it reads and the tools it has. They also take actions across many systems on behalf of a person. That makes review at build time insufficient. You need controls that apply every time an agent acts, which is why governance focuses on runtime permissions, approvals and logs.
Agents have quickly won over developers and business teams. They are autonomous, configurable and increasingly easy to build, which is also what makes them a headache for security and risk teams. Agents carry two independent categories of risk.
Many vendors promise agents that send emails or create Jira tickets. None will cover your legal fees if one of them publishes sensitive information to a public board or emails a customer's personal data to an outside party. Because AI is non-deterministic and small prompt changes can produce very different behavior, the responsibility for protecting the business from agent mistakes sits with the enterprise, especially a regulated one.
The problem also grows on its own. Once teams can build agents easily, they multiply, and nobody has a full picture of what exists. We cover that failure mode in what agent sprawl is and how to prevent it.
Protecting the business comes down to three controls.
An agent should always have an owner and inherit that owner's restrictions, plus any extra ones you add. This is least privilege: only the permissions the agent needs. An owner should never be able to give an agent broader access than they hold themselves. Access control is an old discipline, and agents are subject to whatever model your company already uses, whether role-based, attribute-based or relationship-based.
Can Okta or Entra ID manage AI agent permissions? Identity providers like Okta and Microsoft Entra ID are the right place to authenticate people and manage groups through SSO and SCIM. By themselves they typically don't decide which tool calls an agent may make in Salesforce, Jira or Google Drive, or whether a given action needs approval. Agent governance connects the two: identity from your IdP, plus permissions inherited from each source system, enforced every time an agent calls a tool. A shared service account or admin API key is the pattern to avoid, because every user then acts with the same broad rights and your logs can't say who did what.
With a person, you can ask in Slack who deleted a table. With an agent there is no reliable way to reconstruct history unless every action was recorded as it happened. A useful AI agent audit log captures:
Logs are most useful when they flow into the tools your security team already uses, such as a SIEM. For more detail, see our guide to AI audit logs.
For sensitive actions, a person should approve before the agent proceeds, after seeing a clear summary of what it is about to do. This greatly reduces the odds of a destructive action such as dropping a database or sending a payment. Access and auditing are well-understood. Human-in-the-loop is harder, because people shouldn't have to approve everything or the automation is pointless, yet certain actions must never run unchecked. That requires its own framework.
Not all actions carry the same risk. Some are harmless, some create operational friction if done wrong, and some create financial, legal or compliance exposure. Sort actions into three tiers:
Each tier gets different treatment.
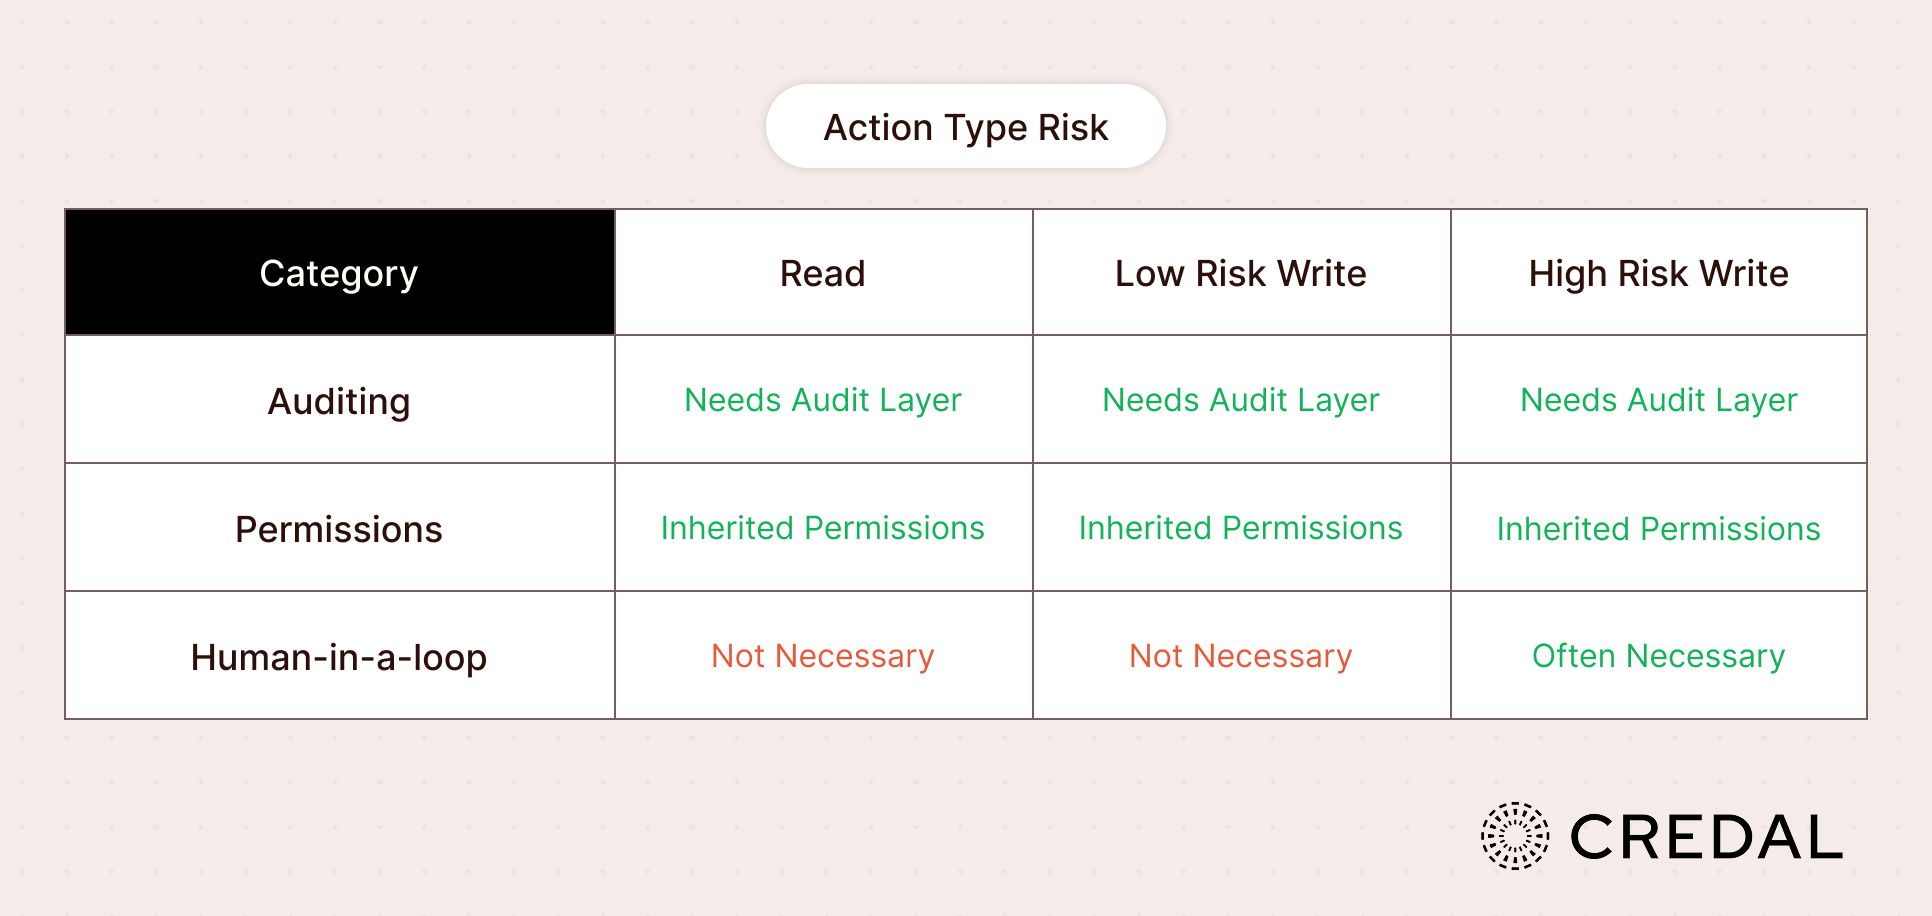
Responsibility flows to the human owner. Through your governance framework, the owner designates the agent's access and can never grant more than they have themselves.
These can usually proceed without approval. With permissions and auditing configured properly, asking a person to approve every action would hinder more than it helps. Accountability falls to the agent's builder.
These should require explicit approval, and accountability falls to the person who approves. Typical examples include payments, outbound email to customers, deleting records, bulk changes and anything touching regulated data.
The enterprise does. Updating a Salesforce record may be low risk while sending a payment is high risk, and only your organization can draw that line. Larger and more regulated companies tend to codify the definitions centrally so they can show a regulator a defensible, repeatable framework. The pattern is covered in more depth in action release gates.
You don't need a large program to begin. When should a company formalize governance? Before agents start writing to business systems, or as soon as more than one team is building them. A practical sequence:
Security teams usually block agents because they can't get answers to a few basic questions. Come prepared with them: who owns each agent, what data it can read, what it can change, which actions need approval, how permissions are inherited, where the audit trail lives and how you can shut an agent off. A governance platform that produces those answers on demand shortens the review considerably.
If you're comparing the best AI agent governance platforms, these questions separate real governance from a dashboard:
Credal is the governance layer that agents run inside. Every tool call goes through Credal's MCP gateway, and every agent is tracked in the Agent Registry.
Credal is SOC 2 Type II and HIPAA compliant, with options from multi-tenant cloud to air-gapped on-prem. See Credal security. Credal doesn't decide what is low or high risk for you. That call belongs to your organization, and Credal enforces whatever rules you set.
Want to see it with your own stack? Get a demo of Credal.
It is the access controls, audit logs and approval rules that decide what AI agents can see and do inside a company and who is accountable for their actions.
At minimum: a named owner for every agent, per-user identity with inherited permissions, human approval for high-risk actions, a complete audit log and a registry of every agent that exists.
AI governance covers policy for all AI systems, including model risk and fairness. AI agent governance is the runtime layer for systems that take actions: who the agent acts as, what it can touch and when a person must approve.
Data exposure to people who shouldn't see it, incorrect or unauthorized changes in business systems, untraceable incidents, shared credentials and uncontrolled growth in the number of agents.
Before agents get write access to business systems, or as soon as more than one team is building them. Retrofitting controls after agents have spread is much harder.
If agents only read public information, probably not. Once they use company data or change systems, you need controls that apply every time an agent acts, which individual tools and prompts can't guarantee on their own.
The enterprise. Vendors rarely accept liability for agent behavior, so companies should assign owners, define which actions need approval and keep records that show who authorized what.
Run agents under the requesting user's identity through SSO instead of a shared service account, and inherit permissions from each source system so the agent can never see or change more than the person can.

One platform for all agents. Full visibility for admins, full access for teams.

One platform for all agents.
Full visibility for admins, full access for teams.